ProtectSMB GRC turns the ISM, Essential Eight, ASD Essentials, NIST CSF, ISO 27001 and SOC 2 into a matrix you can actually work through. Keep a real risk register, audit yourself clause by clause, and see one honest score for how you would fare if the auditor arrived tomorrow — then hand over the reports and documentation they ask for.
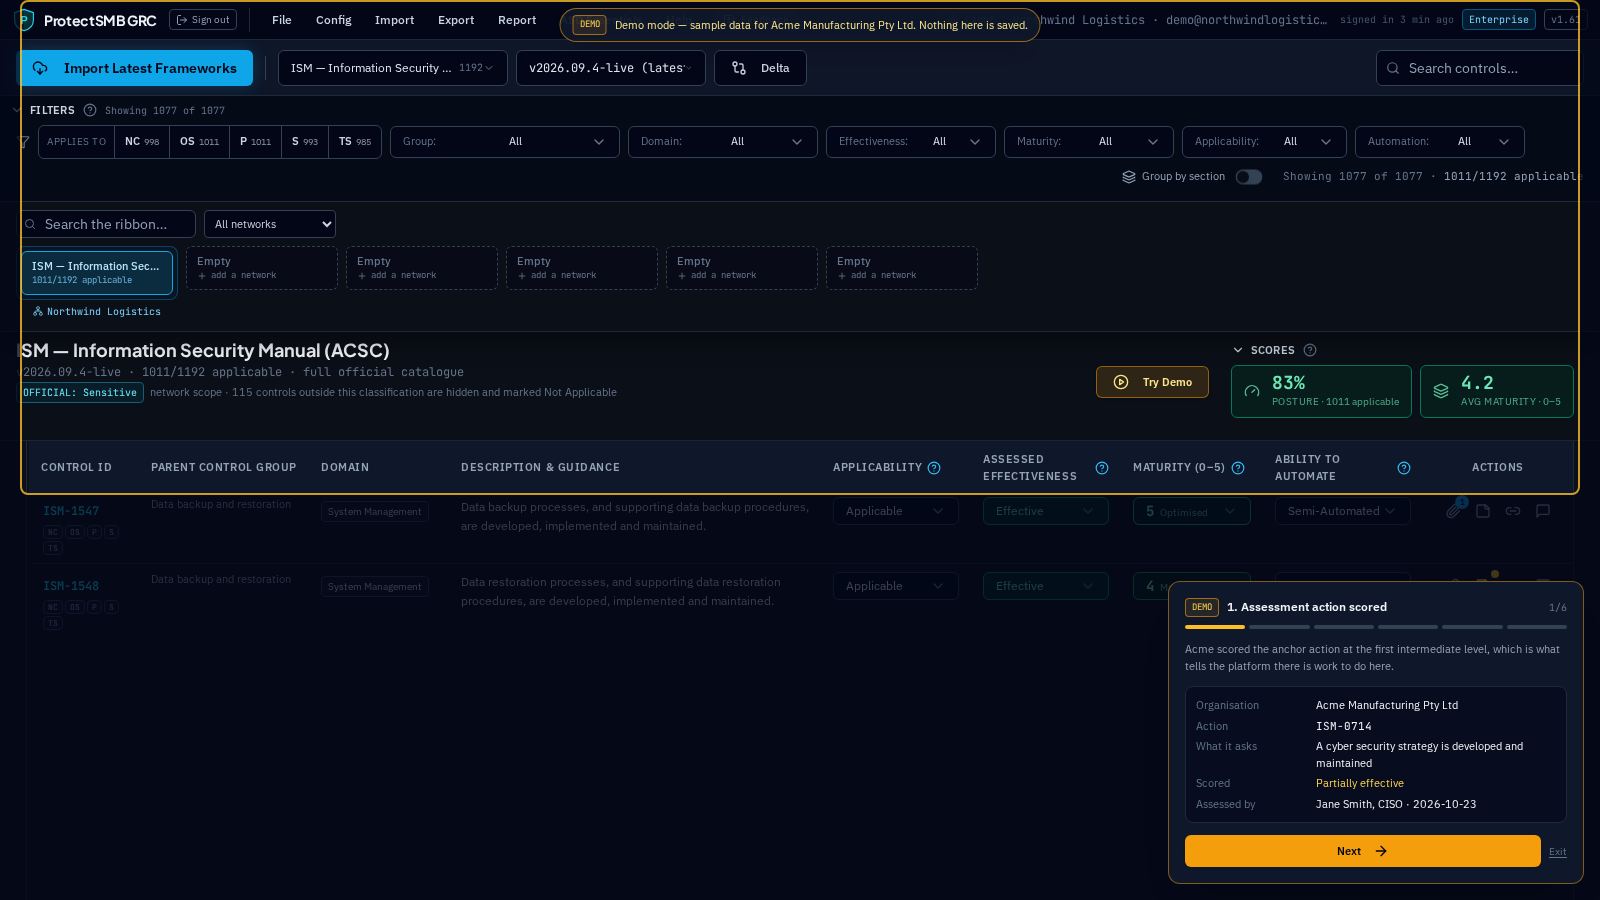
This is the guided demo as it runs inside the product: a real action from the catalogue scored honestly, the evidence behind that score and what it does not cover, the gap that follows, the risk it creates scored before and after treatment, the remediation task with an owner and a due date, and the board report the whole chain lands in.
Step 1 of 6 · Assessment action scored
Acme scored the anchor action at the first intermediate level, which is what tells the platform there is work to do here.
Recorded in the product, captioned step by step — there is no sound to miss. The demo uses sample data for a fictional manufacturer and is kept entirely separate from a workspace's own assessment.
A look inside
Built to be worked in, not admired
Dense where it needs to be, plain where it matters. These are the screens you will spend your time in.
ASD Essentials
Three chapters, in ASD's own words
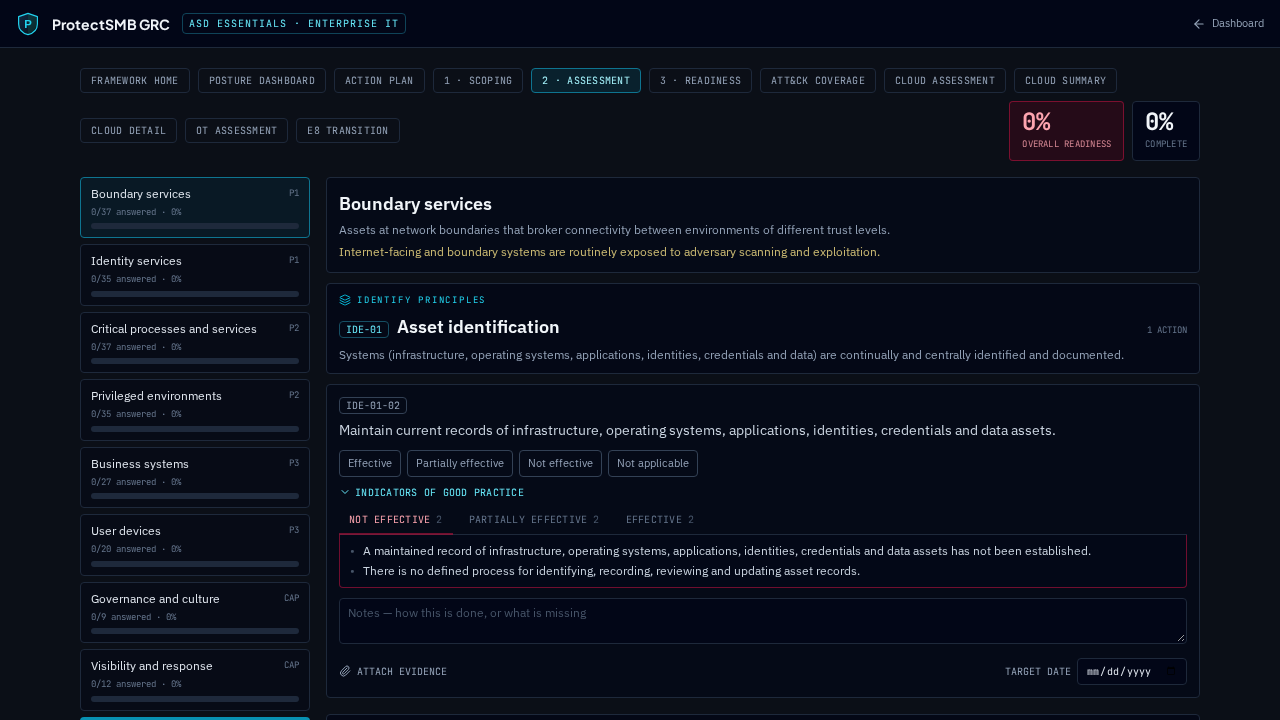
Enterprise IT, operational technology and cloud, each assessed in its own right. The Enterprise IT chapter comes straight from ASD's published catalogue — every principle with its statement, every action with its domains, and ASD's Indicators of Good Practice open beside the score so you can check your call against what ASD says good looks like. Cloud is answered by who is responsible for what; OT asks the hard questions about vital systems, what cannot be patched and whether you could actually run isolated.
Essential Eight maturity
ML1, ML2, ML3 — and the honest answer
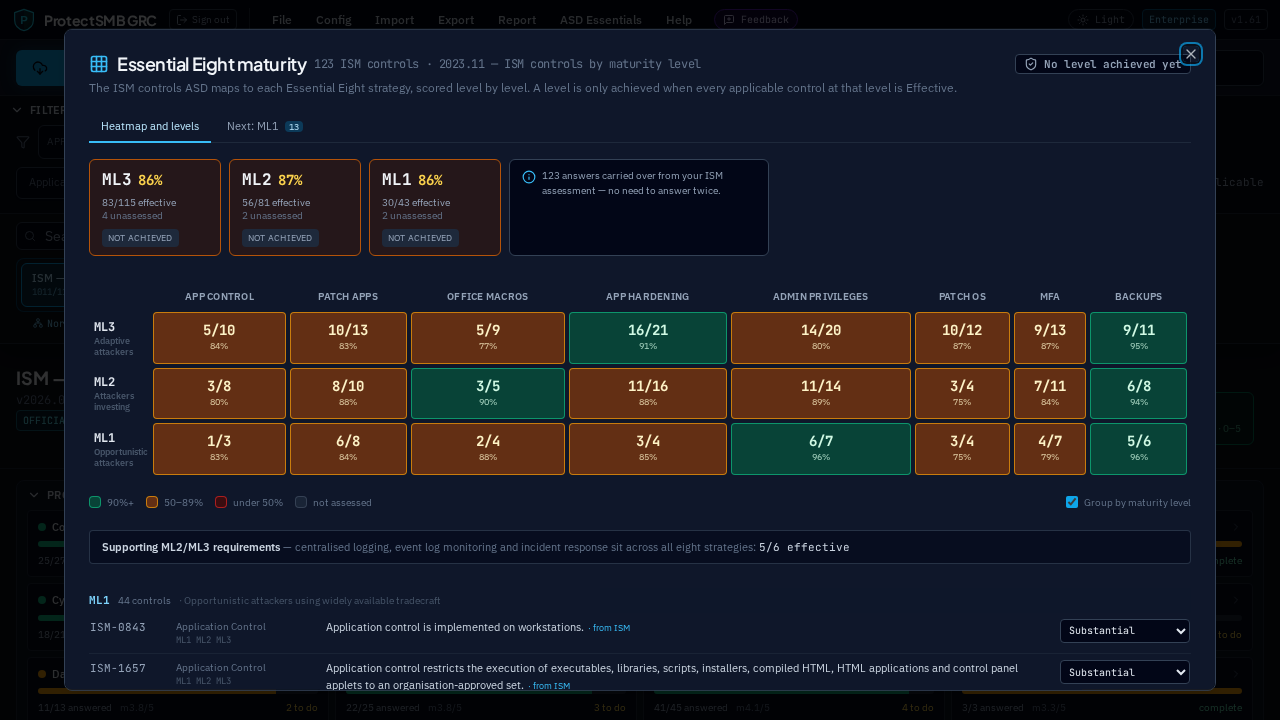
The 123 ISM controls ASD itself maps to the Essential Eight, laid out the way the model is graded: one column per strategy, ML3 on top and ML1 at the base. Each cell is coloured on how many of its applicable controls are genuinely effective, each level carries its own score, and the badge says achieved or not — because ACSC grades a level all or nothing. Click a cell to score the controls behind it, work the checklist for the level you are chasing with a target date on every item, and if you already assess the ISM your answers carry straight across.
The control matrix
Every control, one screen
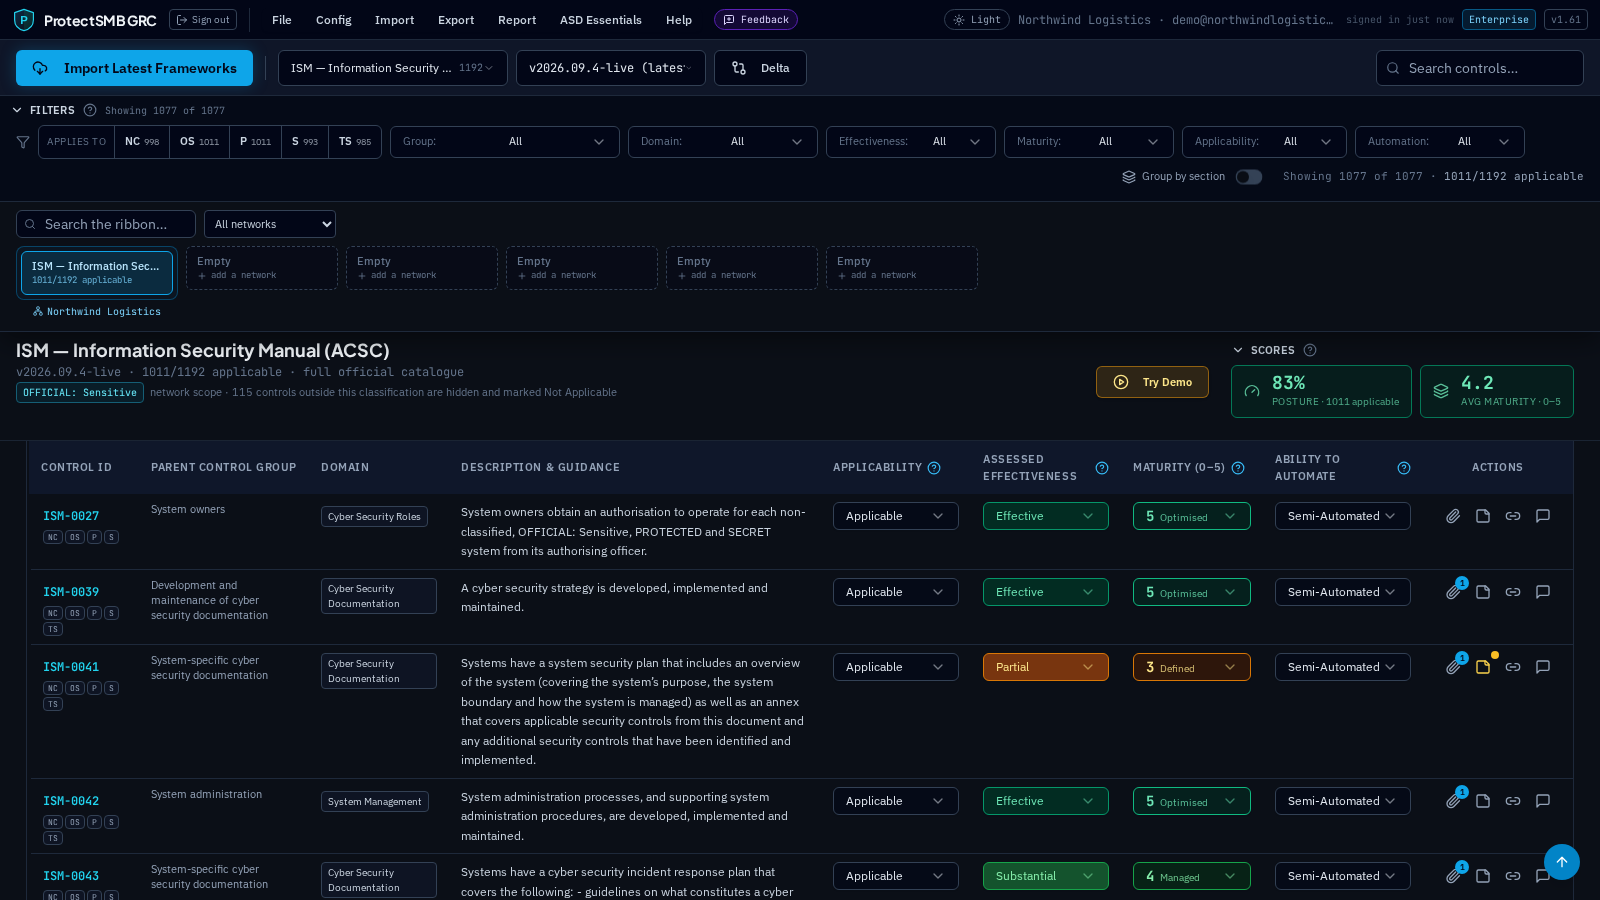
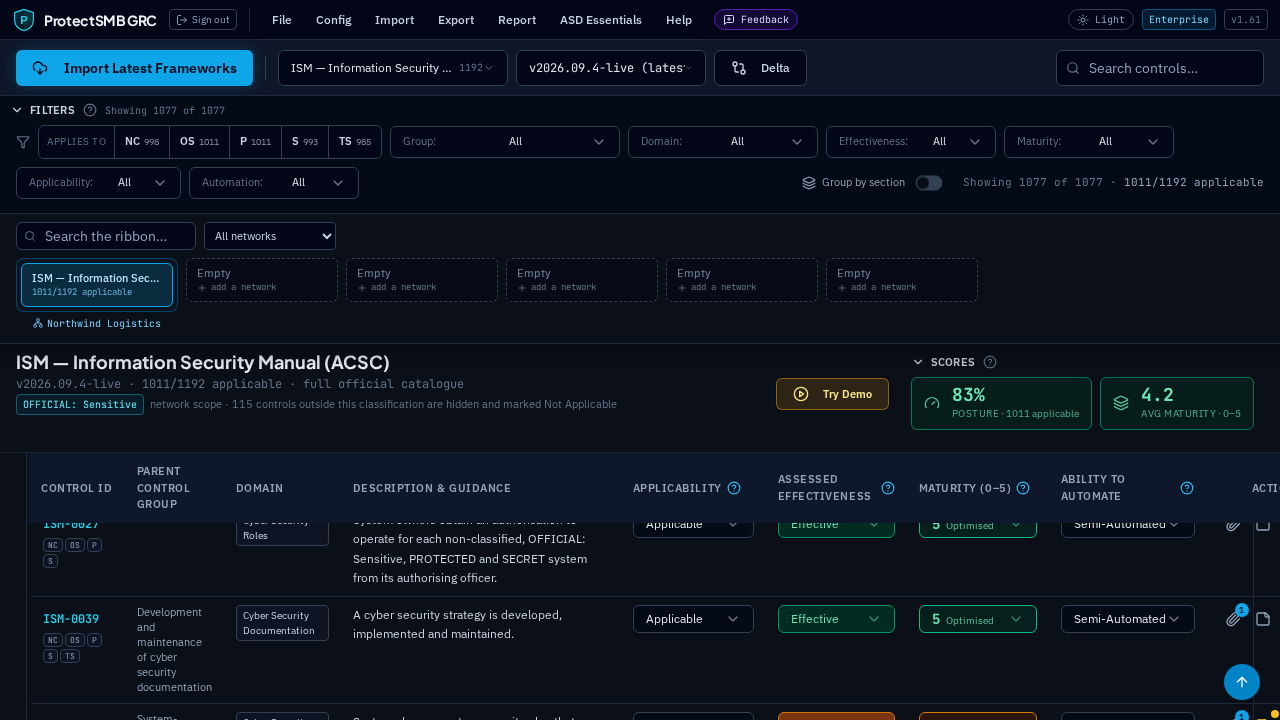
Work through ISM, Essential Eight, ASD Essentials, NIST CSF, ISO 27001 or SOC 2 control by control. Mark what applies, how effective it is and its maturity from 0 to 5. Filter, search and group by section, with the control reference pinned as you scroll.
Posture at a glance
Know where you stand today
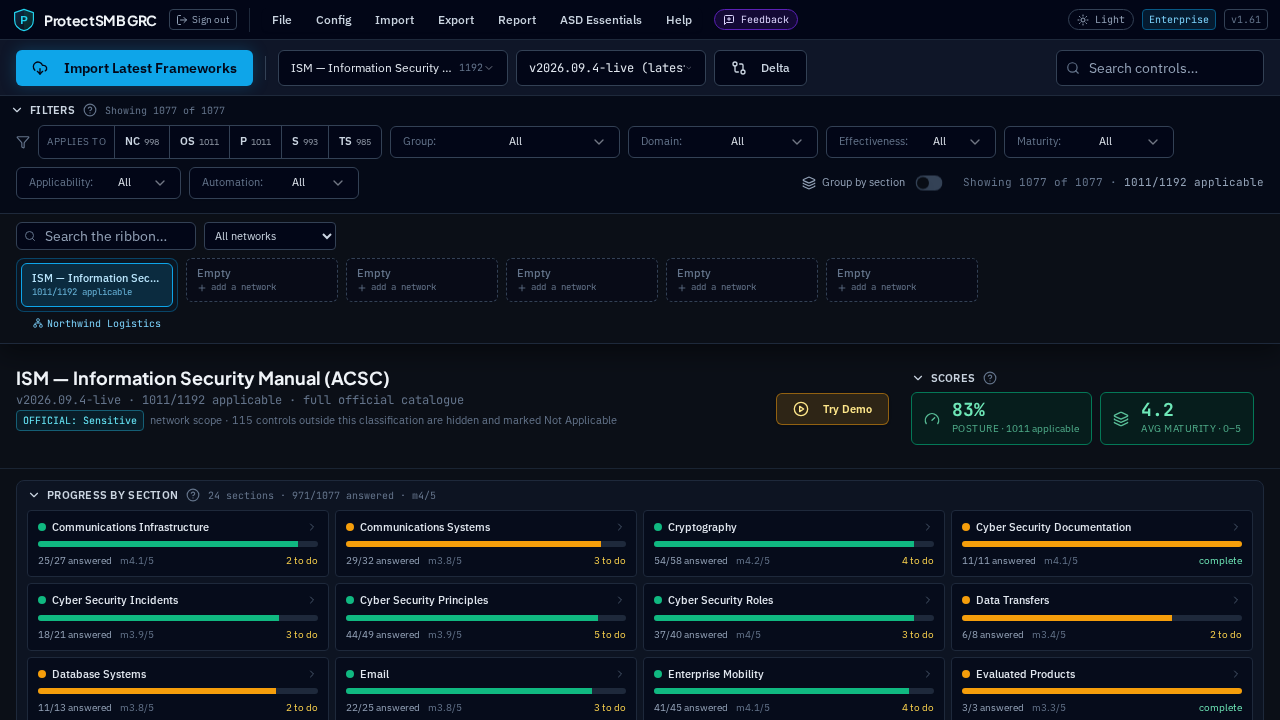
A live posture score and average maturity, broken down by domain, with your gaps and out-of-scope controls counted honestly rather than hidden.
Certification readiness
One honest score, not a vanity metric
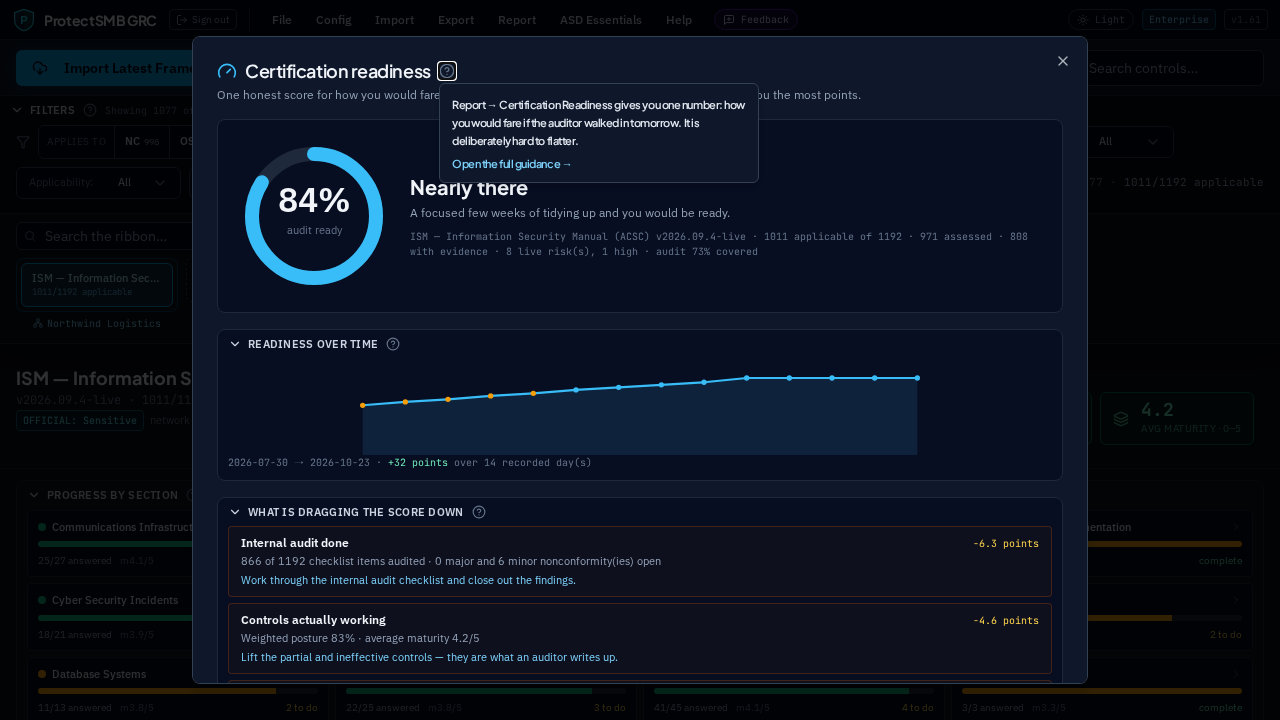
How you would fare if the auditor walked in tomorrow, built from the things they actually check: scope decided, controls assessed, controls genuinely working, evidence on file, your Statement of Applicability, the state of your risk register and your internal audit findings. It names what is costing you the most points and records the score daily, so you can see the line move.
Risk register
The register your auditor asks for first
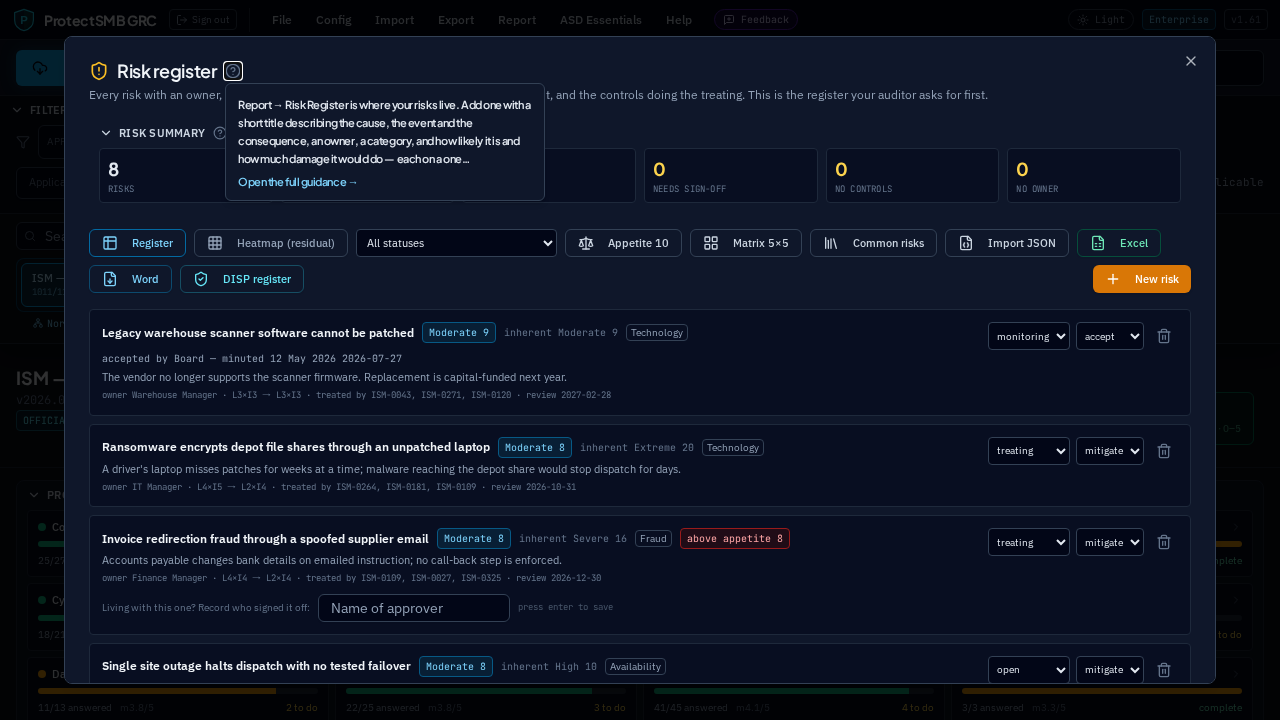
Every risk with an owner, how likely it is and how much it would hurt — scored before treatment and again afterwards — the treatment you have chosen, and the controls doing the treating. Start from the risks nearly every small business carries rather than a blank page, score them on a 3×3, a 5×5 or a grid of your own wording, and set the appetite the board is actually willing to tolerate: anything above it is flagged, and accepting one anyway needs a name and a date against the decision.
Common risks
Start from the risks you already have
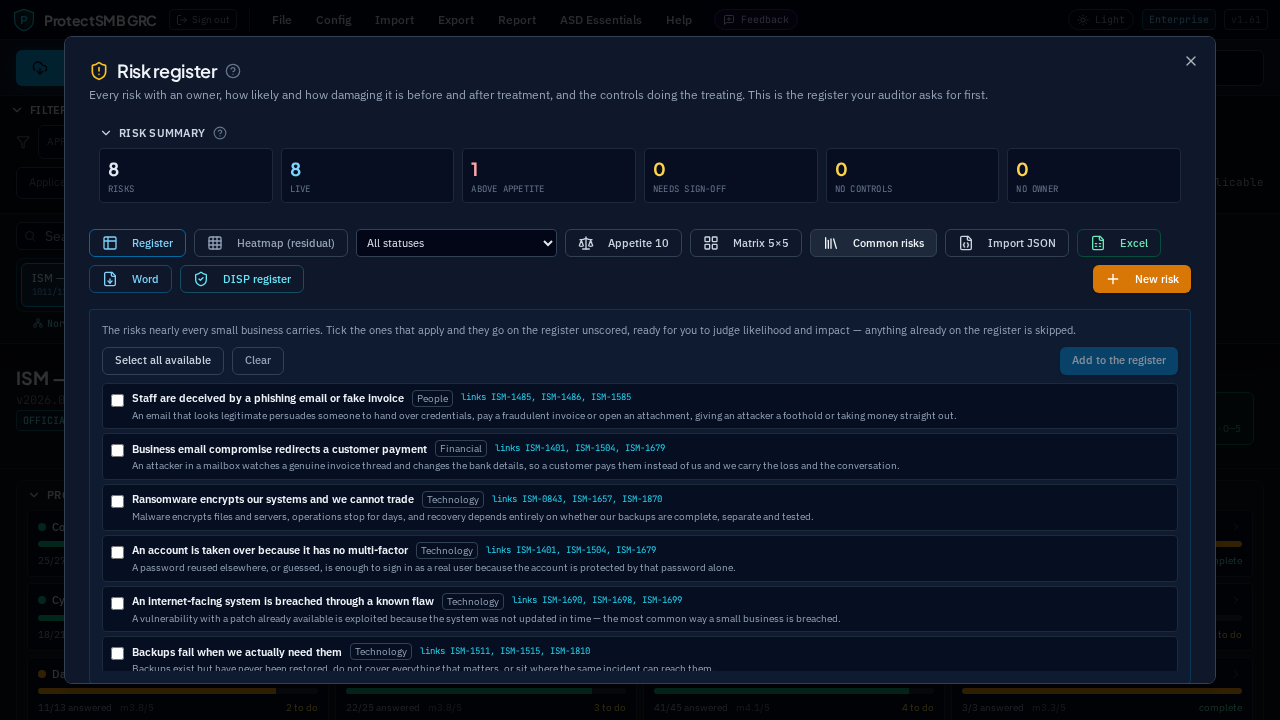
A blank risk register is the reason most never get written. Tick off the risks nearly every small business carries — a staff member deceived by a phishing email, a customer payment redirected, ransomware stopping you trading, an account protected by a password alone, backups that fail when you need them, a departed employee who still has access — and they go on your register unscored, in plain English, with the controls that treat them already linked. How likely and how damaging stays your judgement.
Audit programme
Cover the whole system, a slice at a time
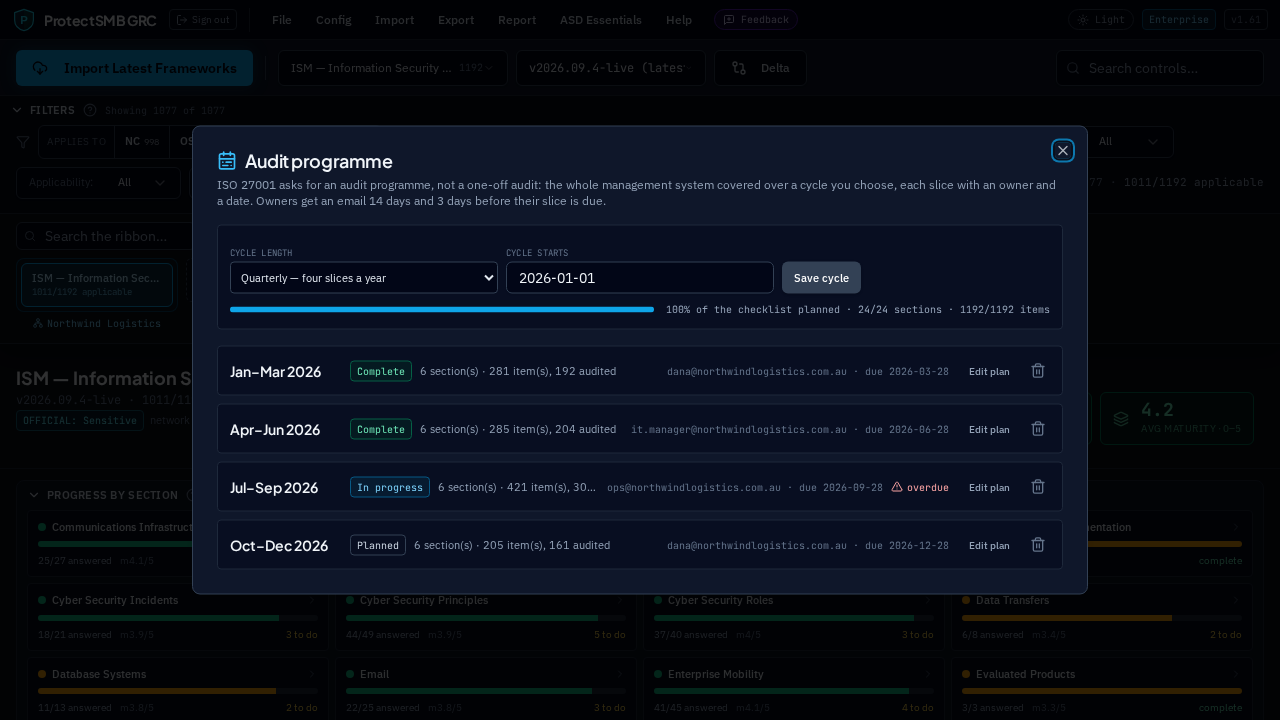
Clause 9.2 asks for an audit programme, not a one-off audit. Choose a monthly, quarterly or half-yearly cycle, assign each period a slice of the system with an owner and a date, and watch the coverage bar until the whole thing is accounted for. Owners get an email 14 days and 3 days before their slice is due, so it happens without you chasing it.
Internal audit
Audit yourself before someone else does
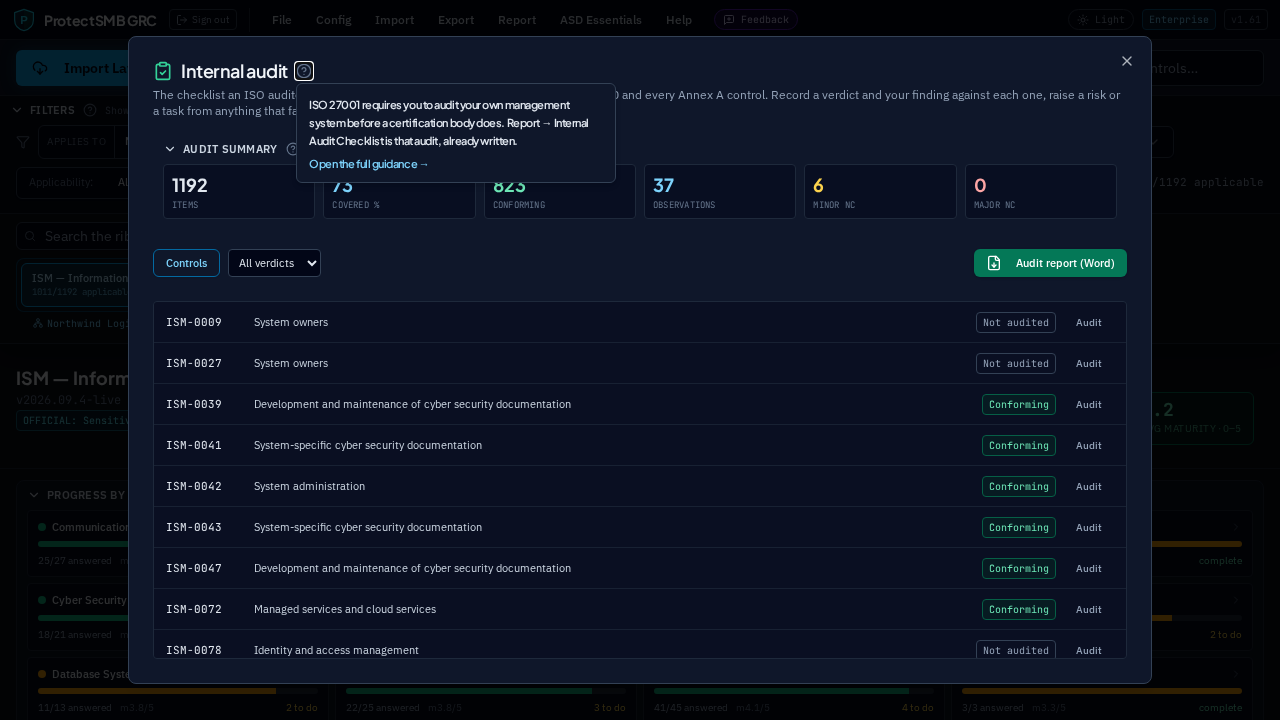
The clause-by-clause checklist an ISO 27001 auditor works through — management system clauses 4 to 10 plus all 93 Annex A controls — each with the question they will ask and what good looks like. Record conforming, an observation, or a minor or major nonconformity, note what you saw, then raise a risk or a remediation task straight from the finding. Hand over the whole thing as a Word report.
Notes and evidence
Capture how you meet each control
Write a short "how we meet this" statement against any control, starting from suggested wording or your own saved snippets, and attach the files that prove it to the evidence vault.
Reporting
Board-ready in one click
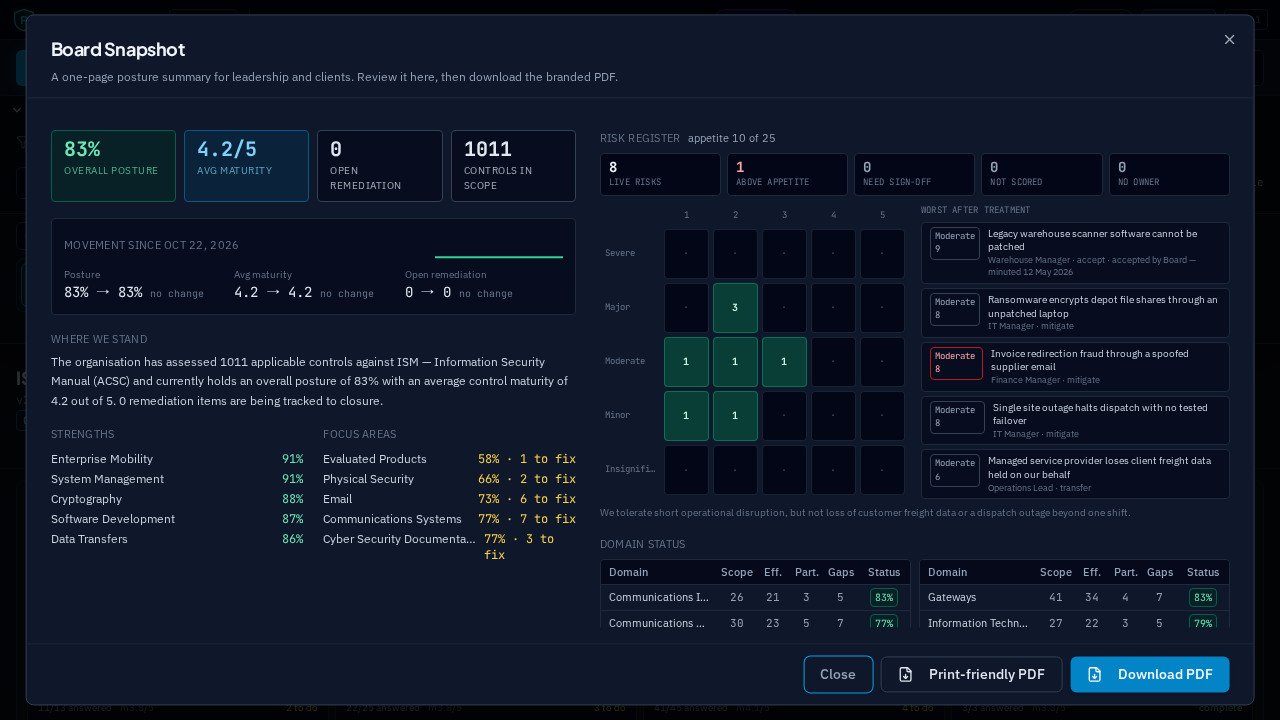
A compliance certificate, an executive summary and a one-page board snapshot — each with a print-friendly version — plus CSV export for your own analysis.
Documentation pack
The paperwork, already written
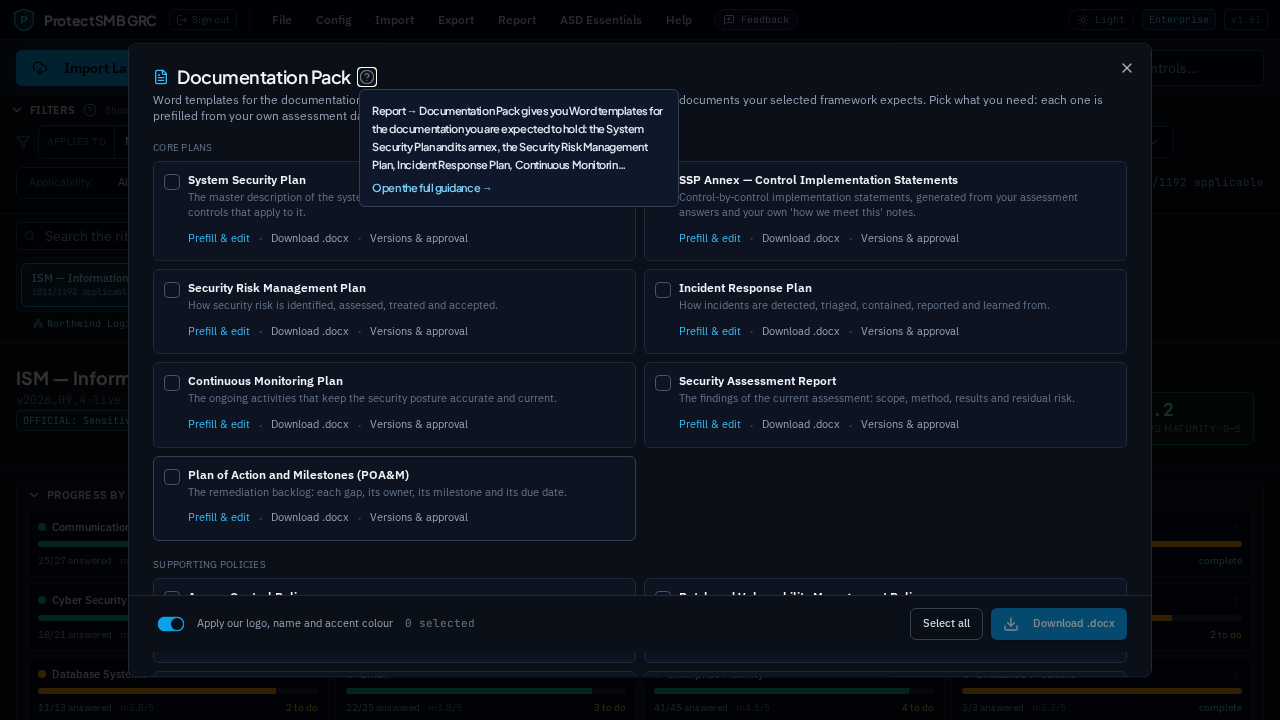
Word templates for the documentation you are expected to hold — the shared policy set plus the documents your framework expects, from the Essential Eight maturity plan to the SOC 2 criteria matrix. Prefilled from your own assessment: org details, posture, maturity, gaps, notes and linked evidence.
Guided demo
See the whole lifecycle before you commit
'Try Demo' walks one real control from your chosen framework all the way through: an honest score, the evidence behind it and what that evidence does not cover, the gap that follows, the risk it creates scored before and after treatment, the remediation task with an owner and a due date, and the board report it all lands in. Each step highlights the part of the screen it describes. It is sample data for a fictional manufacturer, kept separate from your own work and cleared when you leave.
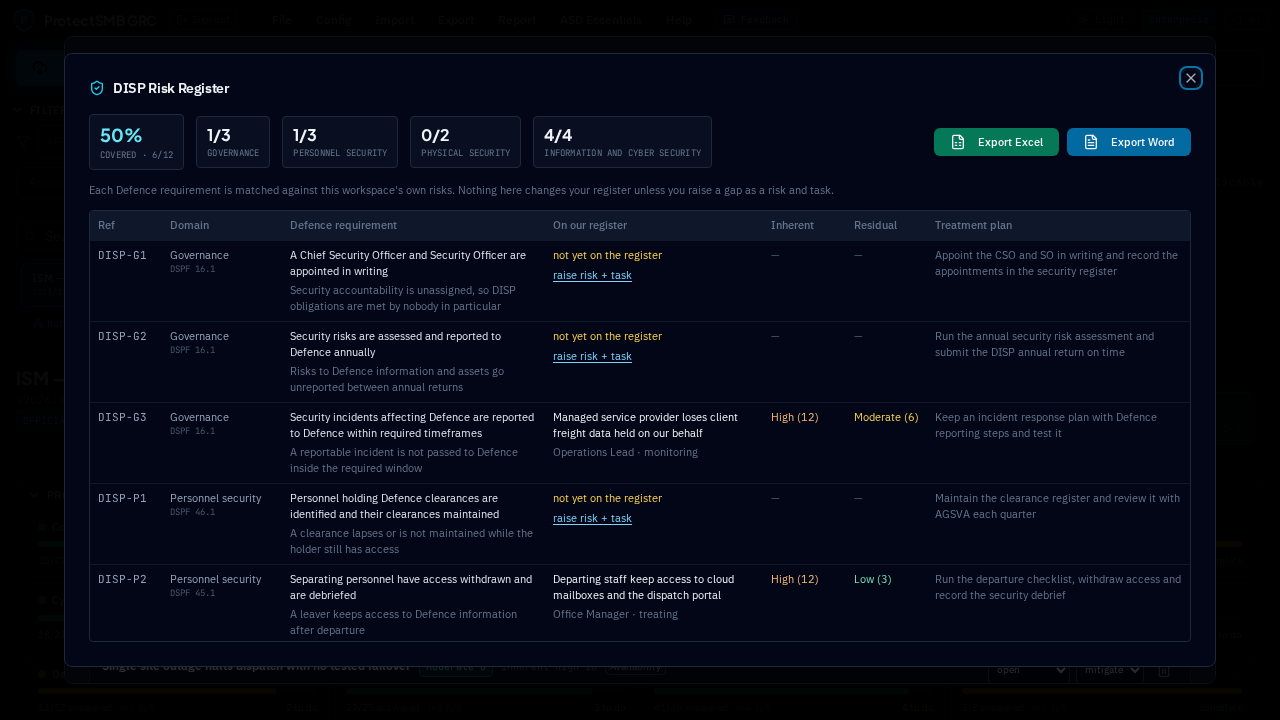
DISP membership
The register Defence expects, measured
Defence Industry Security Programme membership asks you to hold a risk register covering particular ground. Yours is measured against that expectation area by area: what each reference asks for, which of your own risks already answers it, and what is still a gap. Raise a gap and the risk and its remediation task are written for you, worded for that area and linked to the reference. Export the lot as a spreadsheet for your working or a Word document for the pack you hand over.
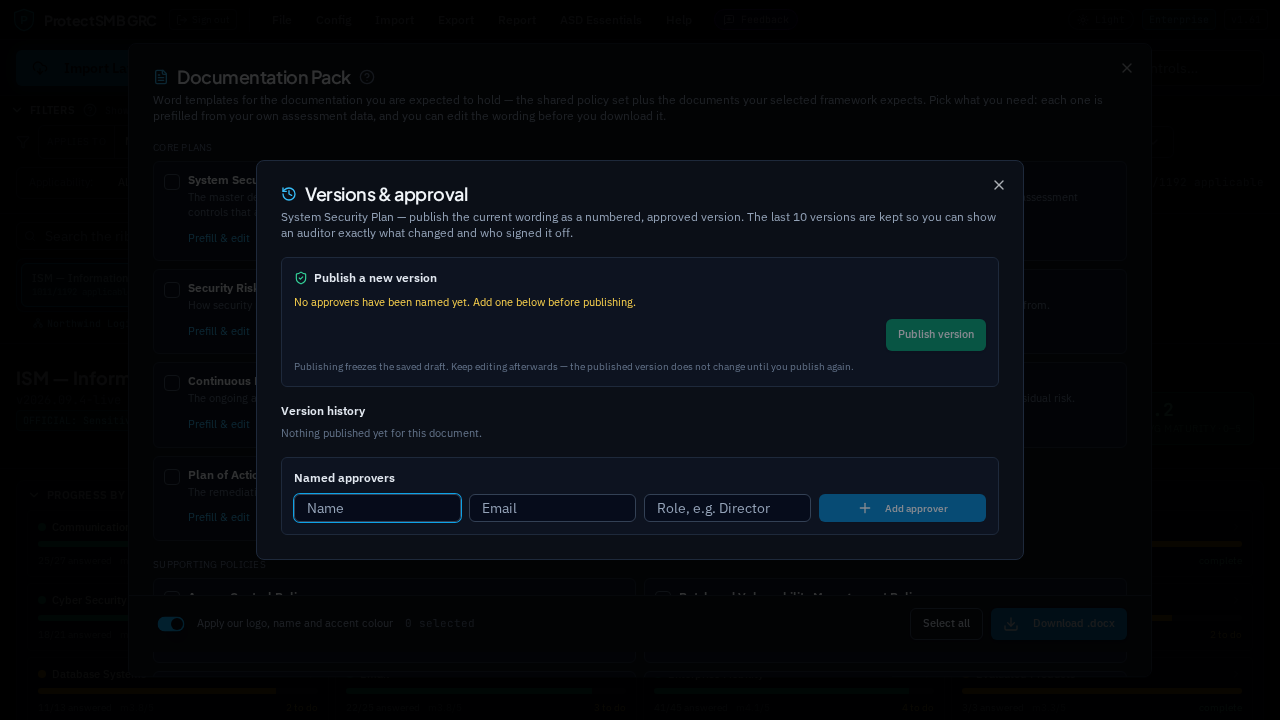
Versions and approval
Show an auditor what changed
Publish numbered versions against a named approver with a review date, compare any two versions line by line, and get a warning before a document is due for review.
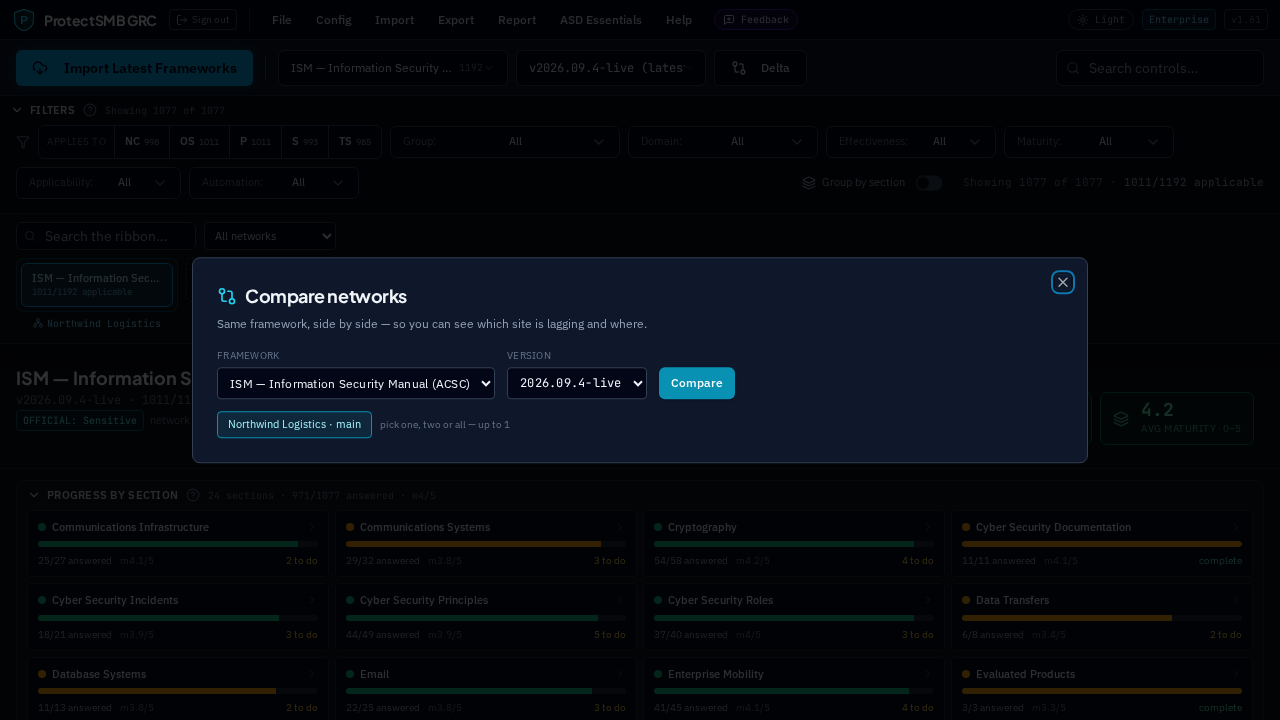
Multiple networks
Run up to six environments side by side
Assess each network, site or environment separately, copy a finished one to a new site as a starting point, and compare two networks control by control to see exactly where they differ.
Everything included
What you can do with it
No modules to buy one at a time. The list below is the product.
ASD Essentials
Three chapters, one programme
Enterprise IT, operational technology and cloud, each with its own actions, scoping and reporting, and one posture view across all three. Included from the Enterprise plan up.
Straight from ASD's catalogue
The Enterprise IT chapter is imported from ASD's official OSCAL catalogue — principles, their statements, every action and its domains — not retyped by us.
Indicators of Good Practice
Every action carries ASD's own rubric: what not effective, partially effective and effective look like, open beside the score as you make the call.
Scored the way ASD words it
Not effective, partially effective, effective, or not applicable — shown as ASD's labels, a number or a percentage, whichever your board reads.
Shared responsibility, inline
Cloud actions are answered by marker: what you own, what the provider supplies and you still operate, and what they perform under assurance evidence you hold.
Operational technology, honestly
Vital OT designated by name, a compensating-controls register for what cannot be patched, break-glass and degraded-state access tested, and an isolation readiness score.
Coming from the Essential Eight
A transition wizard carries every Essential Eight answer across to the ASD Essentials action it satisfies, one confirmation at a time, with the source kept against it.
One action plan
Every chapter's gaps in a single plan with owners and target dates, exportable as Word, PDF or a spreadsheet.
Assess
Six frameworks
ISM, Essential Eight, ASD Essentials, NIST CSF, ISO 27001 and SOC 2, kept current and importable.
Cross-framework mapping
Answer a control once and copy it to the equivalent control in every other framework.
Applicability and scope
Mark controls not applicable or out of scope for your classification, and see the honest applicable count.
Maturity scoring
Rate each control 0 to 5 and track average maturity by domain and over time.
Essential Eight by level
The 123 ISM controls ASD maps to the Eight, scored ML1, ML2 and ML3, with a heatmap of all eight strategies.
Mapping kept current
Re-pull ASD's Essential Eight catalogue, read exactly what changed, and apply it when you are happy.
Level roadmap
Every control between you and your next maturity level, grouped by strategy, with a target date on each and one click to raise the remediation task.
Custom frameworks
Upload your own control set and assess it alongside the standards.
Risk, audit and readiness
Risk register
Every risk with an owner, scored before and after treatment, linked to the controls that treat it.
DISP risk register
Defence Industry Security Programme membership measured area by area: what each reference asks for, which of your risks answers it, and one click to raise what is missing. Exports as a spreadsheet or a Word pack.
Bring your own risk framework
Import an insurer's schedule, a parent company's register or a consultant's workbook as JSON — checked and previewed before a single risk is written, matched on title so nothing duplicates.
The register, in full
Export every risk with its scores, treatment, linked controls, sign-off and review date as a spreadsheet, or the same register as a branded Word document for the board.
Common risks ready to go
Start from the risks nearly every small business carries — phishing, invoice fraud, ransomware, untested backups, a supplier breach — and score them yourself.
Your matrix, your wording
Score on a 3×3, a 5×5 or a grid of your own size, with your own words for every level. Change it and your risks are carried across, not thrown away.
Risk in the board pack
The register, the residual heatmap and your worst five risks printed beside the posture numbers.
Performance monitoring
Response times, error rates, uptime and usage for the whole platform, with email alerts when something slips.
Risk appetite
Set the score the board is willing to tolerate; the heatmap and the register judge against it, not a generic scale.
Sign-off on acceptance
Accepting a risk above appetite needs a name and a date against the decision.
Certification readiness
One honest score for how you would fare if the auditor arrived tomorrow, with the gaps named.
Readiness trend
The score is recorded daily, so you can show progress over weeks rather than claim it.
Internal audit checklist
ISO 27001 clauses 4 to 10 and all 93 Annex A controls, each with the auditor's question.
Audit programme
Plan which part of the ISMS is audited each period of your cycle; owners get reminders before it is due.
Findings that go somewhere
Raise a risk or a remediation task straight from a nonconformity, and download the audit report as Word.
Evidence and remediation
Evidence vault
Attach policies, screenshots and reports to the control they support.
Evidence requests
Track what an auditor has asked for, who owns it and what is still outstanding.
Implementation notes
A short statement per control, with starter wording and reusable snippets.
Evidence in your documents
Every file listed against its control in the SSP Annex, the assessment report and the POA&M.
Remediation tracking
Turn a gap into a task with an owner and a due date, and watch it close.
Audit log
Every change recorded with who, what and when.
Report and prove
Compliance certificate
A signed-off summary of your posture against the framework.
Executive summary
Domain results, priority remediation and what you already do.
Board snapshot
One page your board will actually read, print-friendly if you need it.
Maturity heatmap in the pack
The Essential Eight grid — ML3 to ML1 across all eight strategies — on screen in your board snapshot and printed in it.
Cross-framework coverage
A single view and report showing which frameworks each answer already satisfies.
Documentation pack
Required documentation as Word files, prefilled and version controlled.
Print-friendly output
Every report also comes in an ink-saving layout for handouts and board packs.
Assessor sharing
Give an external assessor a read-only view without creating an account.
For resellers and MSPs
A console of your own
Resellers see every licence they have sold — name, plan, subscription status and renewal date — and nothing else. MSPs get a portfolio of client networks with maturity, gaps and open tasks on every one.
The client invites you in
No provider can claim a workspace. The client raises the invitation, a second administrator of theirs approves it by email, and only then can you accept it. Either side can end it instantly.
Full access or read-only
A client chooses whether you operate on their behalf or only look. Read-only is enforced on every request, not just hidden in the interface.
Your team, their permissions
Invite colleagues on your own domain and set each one's access per client — full, read-only or none, which is where everybody starts. The client approves what you grant.
Slot-based licensing
Six client networks included, then packs of five at a flat $5,000 a year each. A slot is only consumed when you accept a client, and comes back the moment either side ends it.
Deal registration
Register a prospect's domain and we hold it for ninety days. When they sign up, the licence is attributed to you automatically — nothing to claim and nothing to prove.
Partner statements
Download your whole book as a PDF or Word document: every client, their fee, your discount, the net payable and what renews inside ninety days.
Portfolio reporting
A compliance summary across every client, a one-page health report for any single one, and an activity report of everything your people did between two dates.
Run it your way
Multiple networks
Up to six environments per organisation, copied and compared.
AI advice, your key
Implementation guidance from your own OpenAI, Anthropic or Gemini key.
Roles and permissions
Owner, admin, assessor, contributor and viewer, scoped per workspace.
SSO and SCIM
Google sign-in, plus SCIM 2.0 provisioning for Okta and Entra ID.
MFA enforcement
Require multi-factor authentication across the workspace, or of one individual account.
Admins always protected
Anyone given the admin role is required to use two-factor automatically, and cannot be exempted.
New-network approval
Sign-ins from an unfamiliar network are held until an admin approves them, with the trusted starting point under your control.
New-network approval
Refuse sign-ins from an IP range nobody has used before until an admin approves it by email.
Sign-in history
The last five sign-ins for every account, with device, location and IP, in both consoles.
Your branding
Your logo, name and accent colour on every report and document.
Light or dark
A bright theme for boardroom screens, a dark one for daily work.
Documentation, public
A full user guide anyone in the business can read, and download as Word.
A guided demo
Walk one control through scoring, evidence, gap, risk, remediation and the board report before you commit — sample data, kept apart from your own work.
Tell us from inside the app
An idea, a problem, a question or praise goes straight to us with a reference number, without leaving the screen you are on.
White-label deployment
Run the platform under your own name, logo and colours — across the app, emails, PDFs and Word documents.
Modules you choose
Switch each framework, custom uploads and AI on or off per deployment; retiring one never strands existing work.
Sovereign install
A dedicated instance on your own infrastructure — Azure Australia East, Docker on your own Linux host, or Windows Server 2022 with IIS and no Docker at all. Air-gapped if you need it, sending email through your own mail server.
Frameworks and documentation
Six frameworks, documents for each
Every framework below is fully assessable, and each one comes with its own documentation: the shared policy set plus the documents that framework expects — the Essential Eight maturity plan and procedures, the ISO 27001 Statement of Applicability, NIST CSF profiles, the SOC 2 system description and criteria matrix.
ISM
Information Security Manual (ACSC)
assessment · available
documents · available now
Essential Eight
Essential Eight Maturity Model
assessment · available
documents · available now
ASD Essentials
ASD Essentials — Enterprise IT, OT and cloud (ASD)
assessment · available
documents · available now
NIST CSF
NIST Cyber Security Framework
assessment · available
documents · available now
ISO 27001
ISO/IEC 27001 Annex A
assessment · available
documents · available now
SOC 2
Trust Services Criteria (AICPA)
assessment · available
documents · available now
ASD Essentials
The framework government buyers ask about, in all three of its chapters
The Essential Eight stops at eight technical strategies. ASD Essentials goes wider — governance, people, process, plant and cloud — and we carry all three chapters, scored in ASD's own levels and reported chapter by chapter or as one posture across the lot. Included from the Enterprise plan up, and a $1,000 a year add-on below it.
Enterprise IT
58 actions
Imported straight from ASD's published catalogue — every principle with its statement, every action with the domains it protects, and ASD's Indicators of Good Practice open beside the score so your call is judged against ASD's words, not your impression of them.
Operational technology
61 actions
The questions a plant actually turns on: which systems you cannot run safely without, what cannot be patched and what protects it instead, whether break-glass has been tested, and whether you could keep producing while isolated from everything else.
Cloud
78 actions
Answered by who is responsible for what. What you own is scored outright, what the provider supplies has to be enabled, configured and actually used, and what they perform stands on assurance evidence whose scope covers the services you really consume.
Book a walkthrough
Half an hour, screen shared, on your own situation: which chapters apply to you, what the Essential Eight work you have already done carries across, and what the honest size of the gap looks like.
One annual price per workspace, with every user included — no per-seat billing on the first three tiers. Essentials covers the Essential Eight; Professional covers one framework of your choosing, set when you start; Enterprise covers all five. ASD Essentials — the Enterprise IT, operational technology and cloud chapters — is included from Enterprise up, and is a $1,000 a year add-on on Essentials and Professional.
The Essential Eight, scored properly. For a small business that needs to know where it stands.
+ ASD Essentials $1,000 a year
Professional
AUD $1,000
per year, per workspace, ex GST
One framework of your choosing, with remediation tracking and posture history. For a business working towards a single standard.
+ ASD Essentials $1,000 a year
Most complete
Enterprise
AUD $30,000
per year, per workspace, ex GST
All five frameworks at once, plus ASD Essentials included, assessor sharing, audit log, documentation packs, backups and extra networks.
Coming soon
Custom / MSP / Self-hosted
Talk to us
priced per engagement, ex GST
All features, including everything in Enterprise. Every feature in the platform, run your way — your own brand, your own mailbox, and a self-hosted or sovereign install if you need one. Priced per engagement.
Sovereign — dedicated instance
Talk to us
priced on application
All features, including everything in Enterprise. Your own instance of the platform on Australian infrastructure: a dedicated database, your own domain, audit forwarding to your SIEM, and an air-gapped install if you need one. Nothing shared with anyone else.
Dedicated database, yours alone
Hosted in Australia (Azure australiaeast)
Your own domain and certificate
Audit forwarding to your SIEM
Air-gapped or on-premises option
What you get
EssentialsAUD $500
ProfessionalAUD $1,000
EnterpriseAUD $30,000
Custom / MSP / Self-hostedcoming soon
Sovereign — dedicated instanceTalk to us
Frameworks coveredEssential Eight, ISM, ISO 27001, NIST CSF and SOC 2 — ASD Essentials is included from Enterprise up
Essential Eight · ASD Essentials add-on
One of your choosing · ASD Essentials add-on
All five + ASD Essentials
All five + ASD Essentials
All five + ASD Essentials
Assessment matrixScore controls, maturity and applicability
Evidence vaultAttach and store evidence files
Report PDFsCertificate, executive summary and board snapshot
All frameworksEvery framework at once, rather than one
$4,000
ASD EssentialsThe Enterprise IT, operational technology and cloud chapters
add-on $1,000
add-on $1,000
Cross-framework coverageAnswer once, see and apply it across frameworks
$4,000
Live framework fetchPull the latest published control sets
Custom framework importUpload a control set or IRAP worksheet
Remediation tasksAssign, track and chase remediation work
Trends and snapshotsPosture history and trend charts
Assessor sharingShare a read-only assessment with an assessor
$4,000
Audit logFull activity history for the workspace
$4,000
Security alertsEmail alerts on sensitive account activity
$4,000
AI implementation advicePer-control implementation guidance
AI connectorConnect the workspace's own AI provider key
User managementInvite users and manage roles
Single sign-onGoogle SSO
SCIM provisioningDirectory-driven user provisioning
Backup exportDownload a JSON backup
Backup restoreRestore a workspace from a JSON backup
$4,000
Extra networksAssess up to six networks instead of three
$4,000
Documentation packsWord templates for required documentation, prefilled from the assessment
$4,000
On Professional? Buy your way up, one element at a time
Enterprise adds 8 things to Professional. Take any of them on their own for $4,000 a year each — and if you end up wanting all 8, Enterprise at $29,000 costs less than buying them one by one, so that is what you pay.
All frameworks$4,000
Cross-framework coverage$4,000
Assessor sharing$4,000
Audit log$4,000
Security alerts$4,000
Backup restore$4,000
Extra networks$4,000
Documentation packs$4,000
Your workspace admin picks the elements under Compliance → Add to your plan, with a running total as they go. Choose the lot and we move you to Enterprise at the flat $29,000 instead.
Prices are in AUD and exclude GST. Every tier includes unlimited users, AI implementation advice using your own provider key, single sign-on and SCIM provisioning. The Custom / MSP / Self-hosted tier is switched on feature by feature for your engagement. The Sovereign option is the same platform, deployed as a dedicated instance in Australia for you alone — on Azure, on your own Linux host, or on your own Windows Server estate. Talk to us about hosting, air-gapped installs and SIEM forwarding. Our trust and security page answers the questions a security questionnaire usually asks.
Selling or managing this for other businesses?
Managed service providers run a portfolio of client networks from their own console — ten client networks are included with the MSP licence and further networks come in packs of five at a flat AUD 5,000 a year per pack, which no discount touches. A client always invites you in and approves it themselves before you can accept. Resellers sell the licence and leave the client to run it, at a discount agreed with us. Both can register a prospect's domain so the licence is attributed automatically when they sign up, and both can download a statement of their whole book. Tell us which you are and we will set you up.
Get in touch
Book a walkthrough
Pick a time that suits you and we will walk you through the matrix for your framework, the reporting and the documentation pack — against your situation, not a canned demo.
A walkthrough of the matrix against your framework
A sample board snapshot and documentation pack
Help moving an existing spreadsheet assessment across
Already a customer? Sign in and use Help → User Guide.
We use essential cookies only — one to keep you signed in and to protect your session. No advertising or third-party tracking. Read the Privacy Policy.